Blog

Articles tagged WordPress Core

2 articles on this topic.

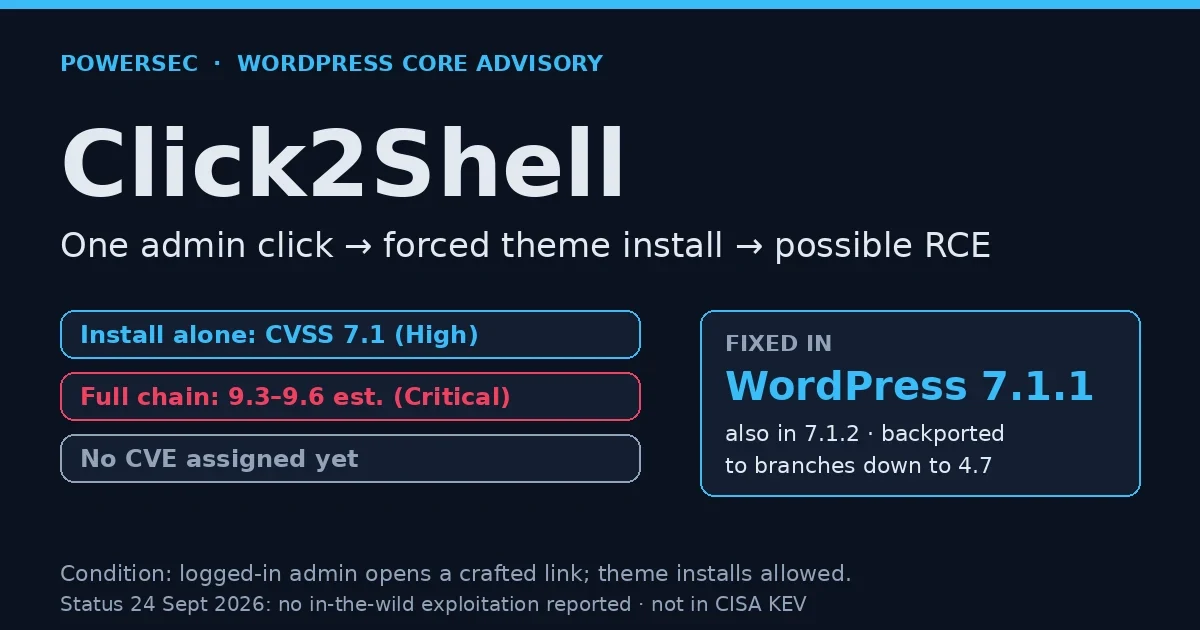
WordPress Click2Shell vulnerability: one crafted link opened by a logged-in admin force-installs a WordPress.org theme, which can chain to remote code execution; fixed in WordPress 7.1.1.
WordPressVulnerabilities

WordPress Click2Shell vulnerability: 1-click theme install to RCE

The WordPress Click2Shell vulnerability lets one admin click force a theme install that can chain to RCE. Update to WordPress 7.1.2 and check your themes.
Oct 1, 2026 · 10 min read
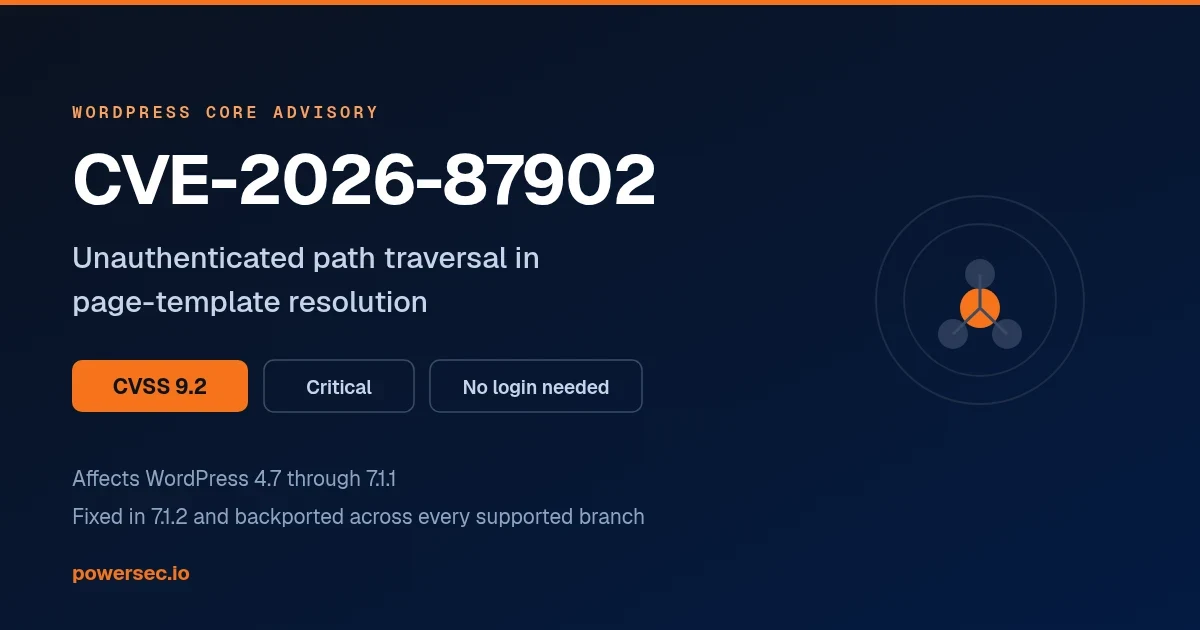
CVE-2026-87902, an unauthenticated path traversal in WordPress page-template resolution. Rated critical at CVSS 9.2, requires no login, affects WordPress 4.7 through 7.1.1 and is fixed in 7.1.2.
WordPressVulnerabilities

CVE-2026-87902: unauthenticated file inclusion in WordPress core

WordPress 7.1.2 closes a critical unauthenticated file inclusion in core, now exploited in the wild. How it works, what makes it code execution, what to check.

Sep 23, 2026 · 15 min read
Hacked? Talk to us