WordPressVulnerabilities
Ninja Forms vulnerability: active attacks and hidden admins
Oct 7, 2026 · 10 min read
5 articles on this topic.
Ninja Forms vulnerability CVE-2026-94504 is under attack alongside WPC Product Bundles. Update affected plugins and check for hidden administrator accounts.
Elementor CSRF vulnerability CVE-2026-62062 affects 4.3.0 and 4.3.1. Update the plugin, verify the fix, and check for unauthorized administrator accounts.
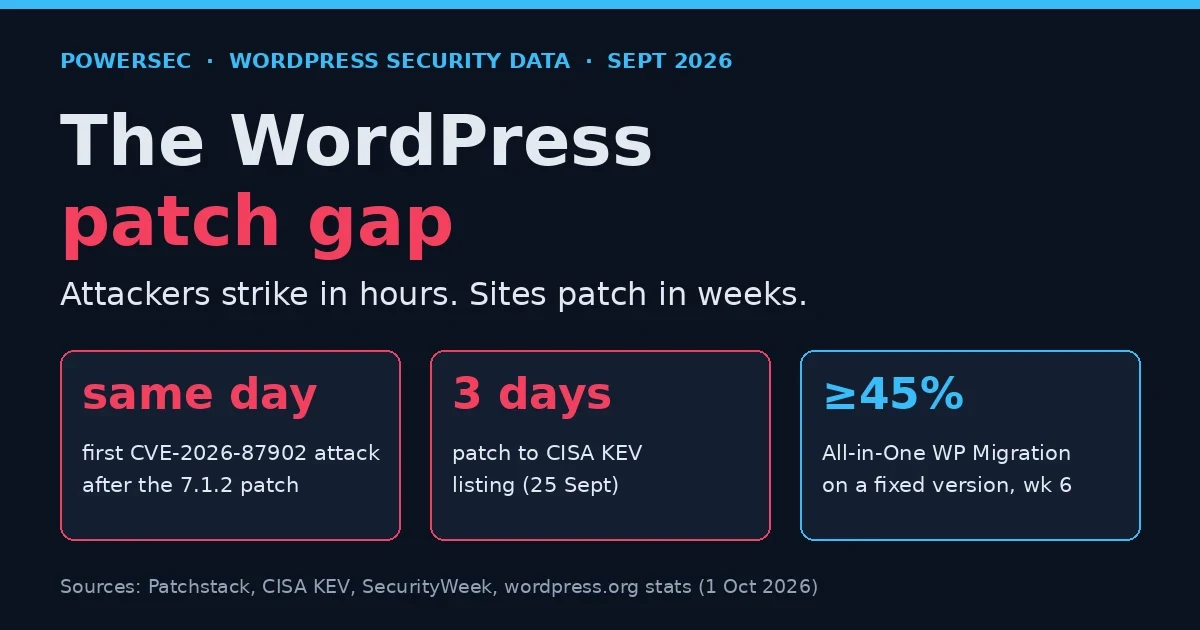
WordPress security updates now race attackers: CVE-2026-87902 was hit the day it was patched and hit CISA KEV in 3 days. See the data and check your sites.
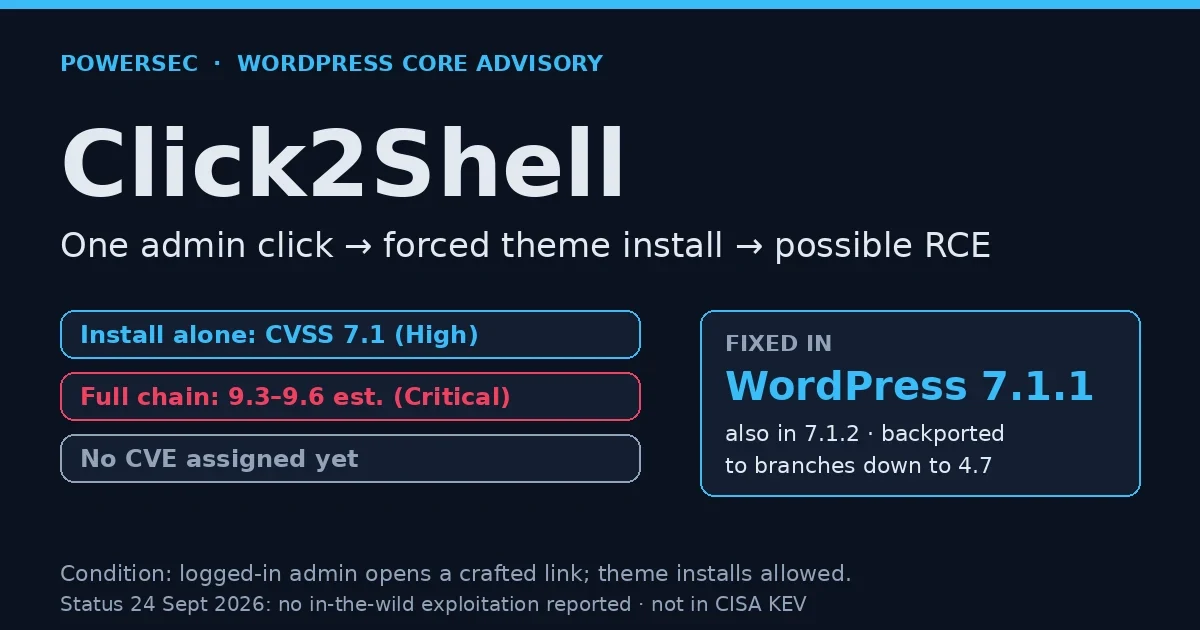
The WordPress Click2Shell vulnerability lets one admin click force a theme install that can chain to RCE. Update to WordPress 7.1.2 and check your themes.
WordPress 7.1.2 closes a critical unauthenticated file inclusion in core, now exploited in the wild. How it works, what makes it code execution, what to check.