WordPressVulnerabilities
Wordfence alternatives: PowerSEC, Sucuri and 3 more
Nov 10, 2026 · 11 min read
Wordfence alternatives: compare PowerSEC, Sucuri, MalCare, Jetpack and Patchstack on security, backups and annual cost. Choose the coverage your site needs.
WP Libre Form has a critical upload flaw, and the 2.0 rewrite can run beside it. Check which plugin is active, disable the old copy, and preserve submissions.
LatePoint vulnerability CVE-2026-118066 can expose booking accounts and linked customer logins. Check both account systems, update, and review access.
Contact Form 7 fixes a file upload flaw, but the patch also changes attachment handling. Check your version, install the update, and test your forms.
Gravity Forms vulnerability CVE-2026-103039 affects versions through 3.1.2. Check post-creation forms and stored data, then install the vendor update.
Checkout Files Upload for WooCommerce has a critical flaw tied to a blank setting. Update the plugin, review allowed file types, and check existing uploads.
PHP2Shell exposes WordPress servers to critical PHP flaws. Check the web runtime, confirm your host's patched build, and update PHP before closing the ticket.
UpdraftPlus security update 1.26.12 revokes old UpdraftCentral keys. Learn what it fixes and what it cannot prove. Update, then review files and access.
Ninja Forms vulnerability CVE-2026-94504 is under attack alongside WPC Product Bundles. Update affected plugins and check for hidden administrator accounts.
Elementor CSRF vulnerability CVE-2026-62062 affects 4.3.0 and 4.3.1. Update the plugin, verify the fix, and check for unauthorized administrator accounts.
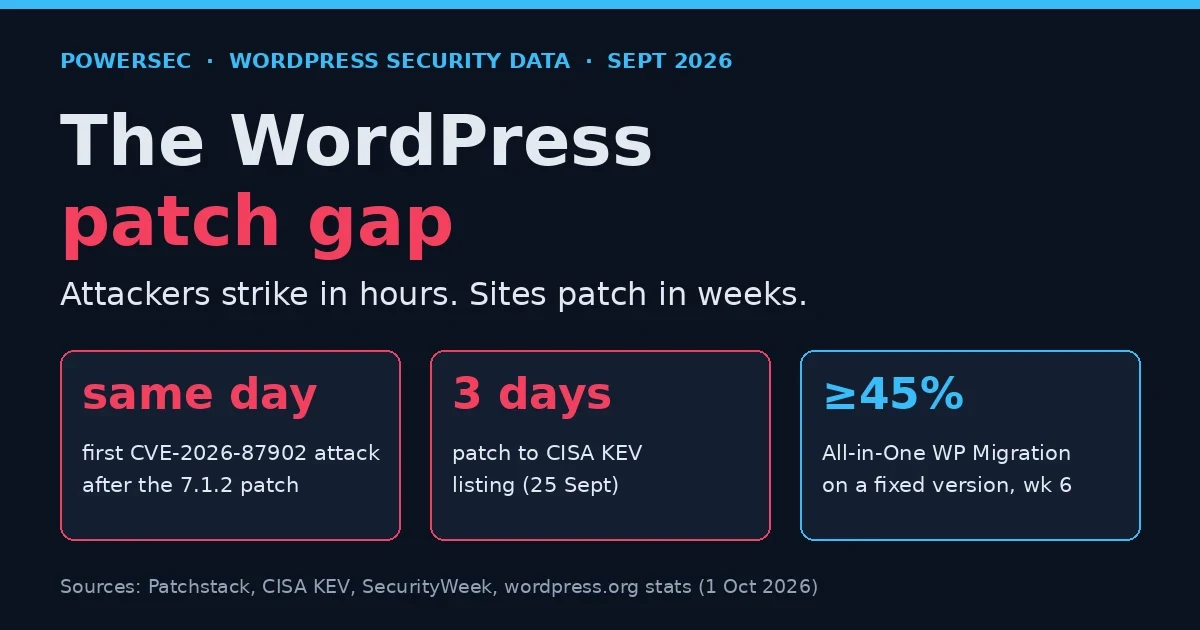
WordPress security updates now race attackers: CVE-2026-87902 was hit the day it was patched and hit CISA KEV in 3 days. See the data and check your sites.
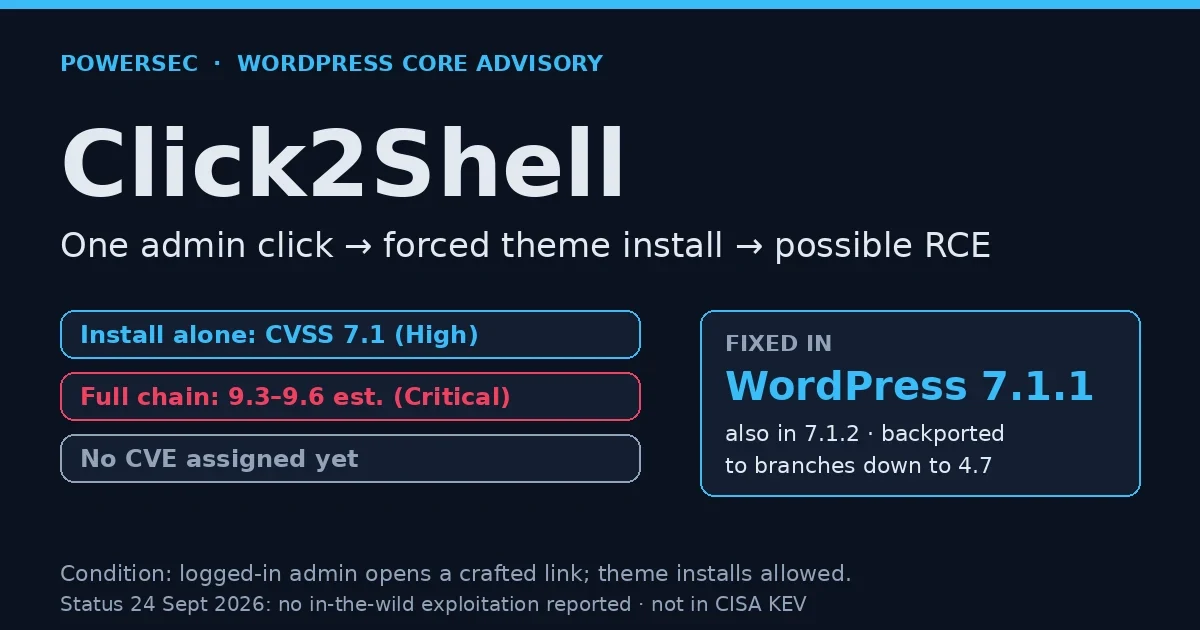
The WordPress Click2Shell vulnerability lets one admin click force a theme install that can chain to RCE. Update to WordPress 7.1.2 and check your themes.