Blog

Articles tagged WordPress

Page 2 of 3. 25 articles on this topic.
Wordfence alternatives illustration showing a WordPress shield, cloud backup vault and management dashboard
WordPressVulnerabilities

Wordfence alternatives: PowerSEC, Sucuri and 3 more

Wordfence alternatives: compare PowerSEC, Sucuri, MalCare, Jetpack and Patchstack on security, backups and annual cost. Choose the coverage your site needs.
Nov 10, 2026 · 11 min read
WP Libre Form illustrated by two cartridges still connected to one chassis, one dark and one cyan
WordPressVulnerabilities

WP Libre Form RCE: Why Installing 2.0 Can Leave 1.5 Active

WP Libre Form has a critical upload flaw, and the 2.0 rewrite can run beside it. Check which plugin is active, disable the old copy, and preserve submissions.
Nov 10, 2026 · 9 min read
LatePoint vulnerability illustration showing a booking calendar and separate customer profile cards beside the words Your Other Login
WordPressVulnerabilities

LatePoint vulnerability: The Customer Accounts You Might Miss

LatePoint vulnerability CVE-2026-118066 can expose booking accounts and linked customer logins. Check both account systems, update, and review access.
Nov 8, 2026 · 10 min read
Contact Form 7 update illustration showing an attachment beside a checked form and the words Patched. Form tested?
WordPressVulnerabilities

Contact Form 7 Security Fix: Don't Stop at the Update

Contact Form 7 fixes a file upload flaw, but the patch also changes attachment handling. Check your version, install the update, and test your forms.
Nov 5, 2026 · 9 min read
Gravity Forms vulnerability illustration showing a magnifying glass over a red-marked field on stacked form cards
WordPressVulnerabilities

Gravity Forms vulnerability: Why 3.1.2 Is Still at Risk

Gravity Forms vulnerability CVE-2026-103039 affects versions through 3.1.2. Check post-creation forms and stored data, then install the vendor update.
Oct 31, 2026 · 9 min read
Checkout Files Upload illustration showing a shopping cart beside an upload panel with a red-outlined empty settings field.
WordPressVulnerabilities

Checkout Files Upload: The Blank Setting Behind a Critical Flaw

Checkout Files Upload for WooCommerce has a critical flaw tied to a blank setting. Update the plugin, review allowed file types, and check existing uploads.
Oct 29, 2026 · 9 min read
PHP2Shell server illustration with a red fault in the runtime layer behind a website
WordPressVulnerabilities

PHP2Shell: Is Your WordPress Server Actually Patched?

PHP2Shell exposes WordPress servers to critical PHP flaws. Check the web runtime, confirm your host's patched build, and update PHP before closing the ticket.
Oct 22, 2026 · 10 min read
UpdraftPlus security illustration of a cyan key beside a cloud and a red warning mark
WordPressVulnerabilities

UpdraftPlus security: update 1.26.12, then check for backdoors

UpdraftPlus security update 1.26.12 revokes old UpdraftCentral keys. Learn what it fixes and what it cannot prove. Update, then review files and access.
Oct 19, 2026 · 10 min read
Ninja Forms vulnerability artwork showing a form beside an account list, with a magnifying glass highlighting a red user icon.
WordPressVulnerabilities

Ninja Forms vulnerability: active attacks and hidden admins

Ninja Forms vulnerability CVE-2026-94504 is under attack alongside WPC Product Bundles. Update affected plugins and check for hidden administrator accounts.
Oct 6, 2026 · 10 min read
Elementor CSRF vulnerability CVE-2026-62062: update the plugin and review account access
WordPressVulnerabilities

Elementor CSRF vulnerability: CVE-2026-62062 patch and checks

Elementor CSRF vulnerability CVE-2026-62062 affects 4.3.0 and 4.3.1. Update the plugin, verify the fix, and check for unauthorized administrator accounts.
Oct 1, 2026 · 10 min read
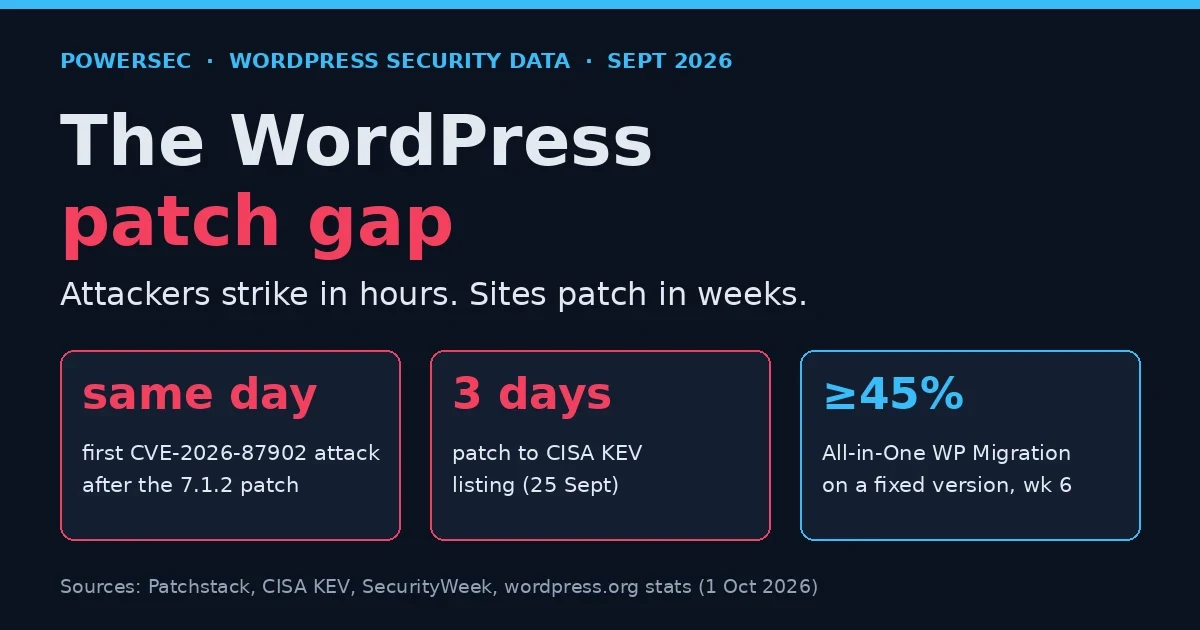
WordPress patch gap in September 2026: attackers probed sites for CVE-2026-87902 within hours of the 7.1.2 security update, while plugin patch adoption took weeks.
WordPressVulnerabilities

WordPress patch gap: hackers strike in hours, sites patch in weeks

WordPress security updates now race attackers: CVE-2026-87902 was hit the day it was patched and hit CISA KEV in 3 days. See the data and check your sites.
Oct 1, 2026 · 11 min read
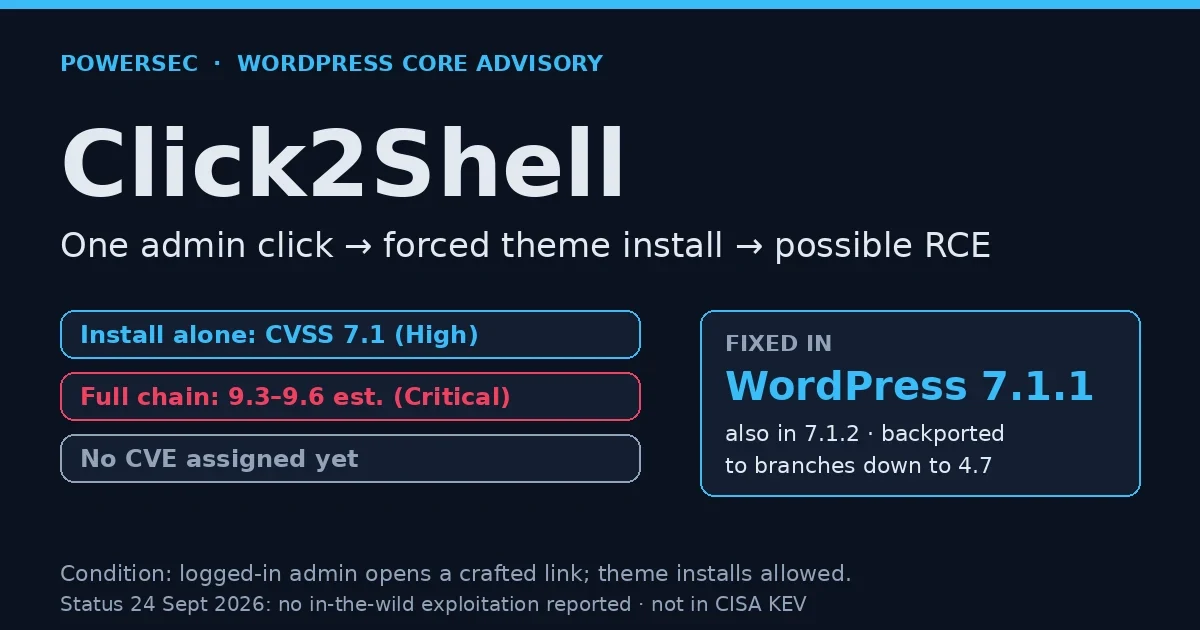
WordPress Click2Shell vulnerability: one crafted link opened by a logged-in admin force-installs a WordPress.org theme, which can chain to remote code execution; fixed in WordPress 7.1.1.
WordPressVulnerabilities

WordPress Click2Shell vulnerability: 1-click theme install to RCE

The WordPress Click2Shell vulnerability lets one admin click force a theme install that can chain to RCE. Update to WordPress 7.1.2 and check your themes.

Oct 1, 2026 · 11 min read
Hacked? Talk to us